When investigating novel 0-days leads to the discovery of novel 0-days
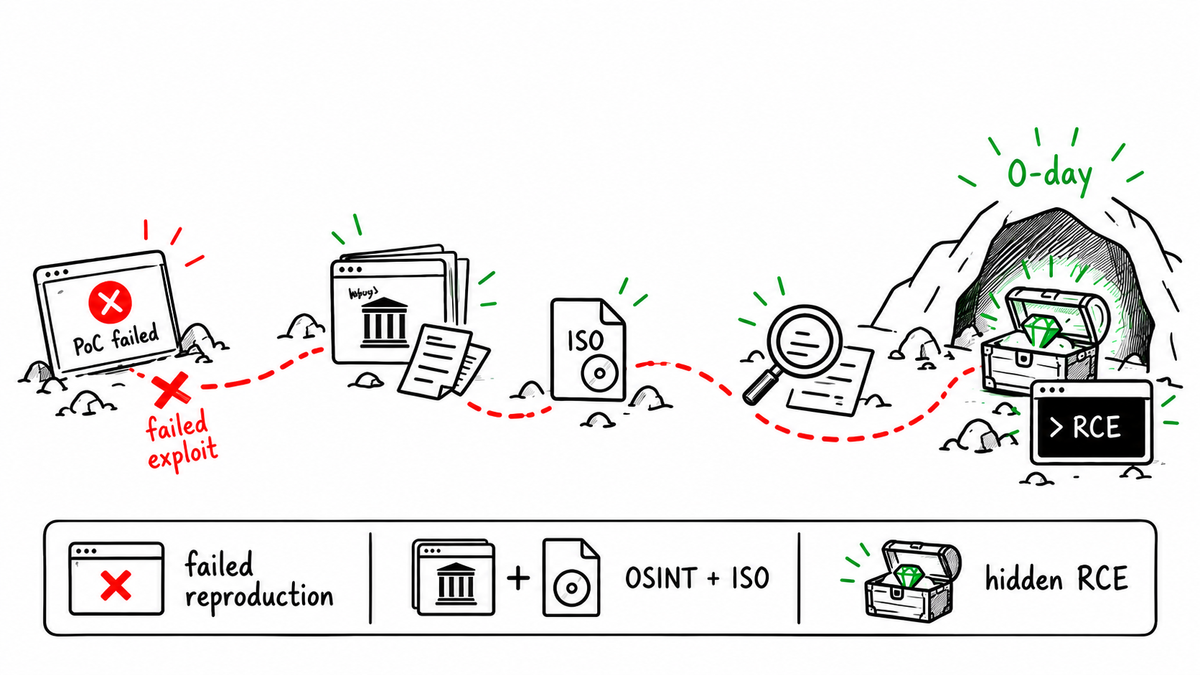
Telenia TVox is susceptible to Unauthenticated OS Command Injection in the /reportExporter/Export endpoint. In this blog post, we discuss how, while investigating previously disclosed TVox vulnerabilities with Claude Code, the AI autonomously discovered a novel unauthenticated RCE, and how we manually validated it on TVox 24 and 26.
Summary
- Product
- TVox
- Vendor
- Telenia Software
- Affected Version(s)
- Confirmed vulnerable: 24.8.4 and 26.5.3 (the complete affected range has not been independently established)
- First Patched Version
- 24.3.47 LTS, 24.9.24, 26.2.14 LTS
- Impact
- The vulnerability allows unauthenticated attackers to inject arbitrary OS commands through the
/reportExporter/Exportendpoint, achieving remote code execution on the underlying server. Combined with a separately described local privilege escalation, command execution as the application user should be treated as equivalent to root. - CVE
- Pending (MITRE request #CAN-2026-2035300)
Abstract
While investigating previously disclosed vulnerabilities in Telenia TVox, we used Claude Code to analyze an older version of the software. Instead of finding an alternative authentication bypass, the AI autonomously discovered a new Unauthenticated Remote Code Execution (CWE-78) in the
/reportExporter/Exportendpoint. We manually verified the finding on both TVox 24 and 26, confirming a previously unknown zero-day affecting even the latest release at the time.
You can read the full article on the SicuraNext blog.